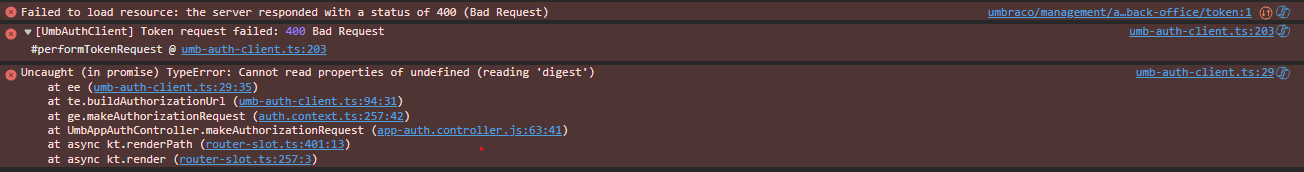
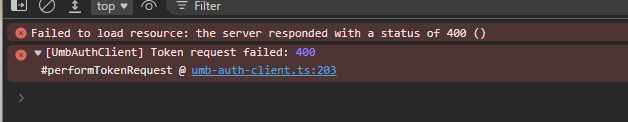
Hi, I am trying to host a test umbraco 17 microsite on IIS 10 Windows 2016 server using http. But when I try to access Umbraco backoffice getting below error:
"@mt":"The token request was rejected because the mandatory '{Parameter}' parameter was missing.","@tr":"d70ff9d3c1c3d69b83c805a799072a01","@sp":"c2c5c7e983e66a18","Parameter":"refresh_token","EventId":{"Id":6077},"SourceContext":"OpenIddict.Server.OpenIddictServerDispatcher","RequestId":"80000002-0001-f800-b63f-84710c7967bb","RequestPath":"/umbraco/management/api/v1/security/back-office/token","ProcessId":7648,"ProcessName":"w3wp","ThreadId":16,"ApplicationId":"e61a0bf26d24318a61231e8716ab3e597eb2fbd6"

"@mt":"The request was rejected because an invalid HTTP method was specified: {Method}.","@tr":"29b65a33d676cb489e538f2fba1098b7","@sp":"4aeca1744d7806d2","Method":"GET","EventId":{"Id":6137},"SourceContext":"OpenIddict.Server.OpenIddictServerDispatcher","RequestId":"80000009-0000-f800-b63f-84710c7967bb","RequestPath":"/umbraco/management/api/v1/security/back-office/token","ProcessId":7648,"ProcessName":"w3wp","ThreadId":34,"ApplicationId":"e61a0bf26d24318a61231e8716ab3e597eb2fbd6"
I think you get that log message as you aren’t currently logged into the backoffice, eg it didn’t find a refresh_token in the current authentication cookie (you don’t have one)
You’ll see lots of these, and are completely normal.. like
js bubbling up the
[12:17:19 INF] The request URI matched a server endpoint: Token.
[12:17:19 INF] The token request was successfully extracted: {
“client_id”: “umbraco-back-office”,
“redirect_uri”: “https://localhost:44335/umbraco/oauth_complete”,
“grant_type”: “refresh_token”,
“refresh_token”: “[redacted]”
}.
[12:17:20 INF] The response was successfully returned as a JSON document: {
“error”: “invalid_grant”,
“error_description”: “The specified refresh token is no longer valid.”,
“error_uri”: “https://documentation.openiddict.com/errors/ID2018”
}.
If you are using the Production runtime mode then you may have to disable that https healthcheck, but the source code seems to suggest setting useHttps :false should be enough, though I haven’t tried that myself, just less hassle to generate a free ssl as required.